
Security & Privacy Insights
Expert perspectives on VAPT, threat research, privacy law, and building secure organizations — from the StateCheck Security team.
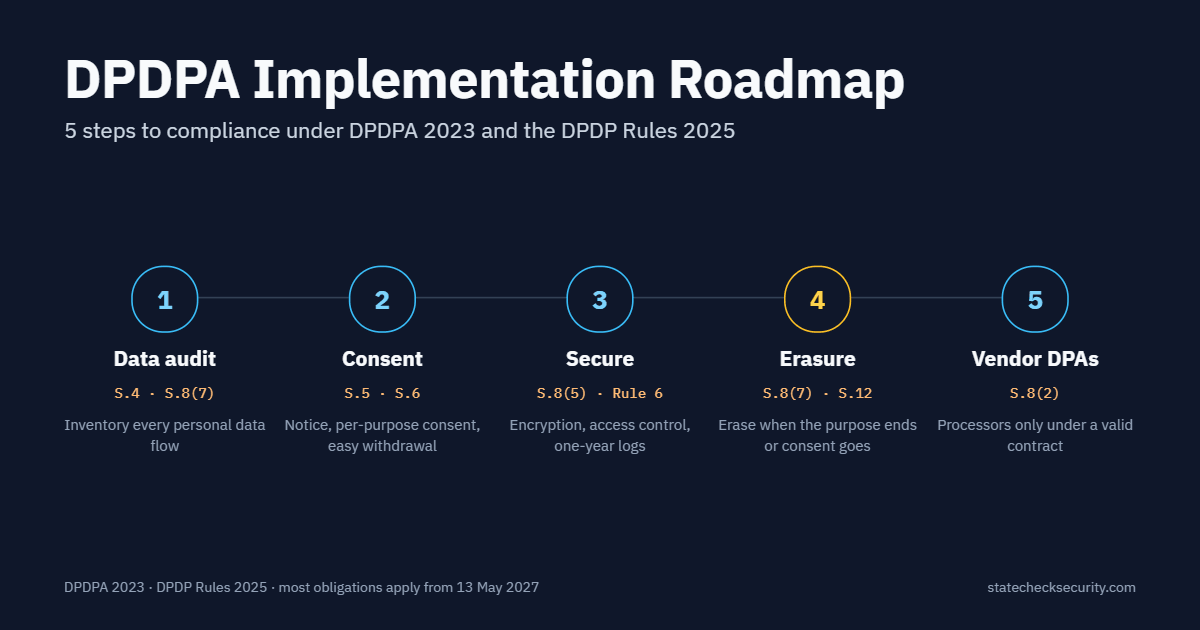
DPDPA Implementation Roadmap: 5 Steps to Compliance
Key Takeaways - A DPDPA implementation roadmap begins with a data audit.
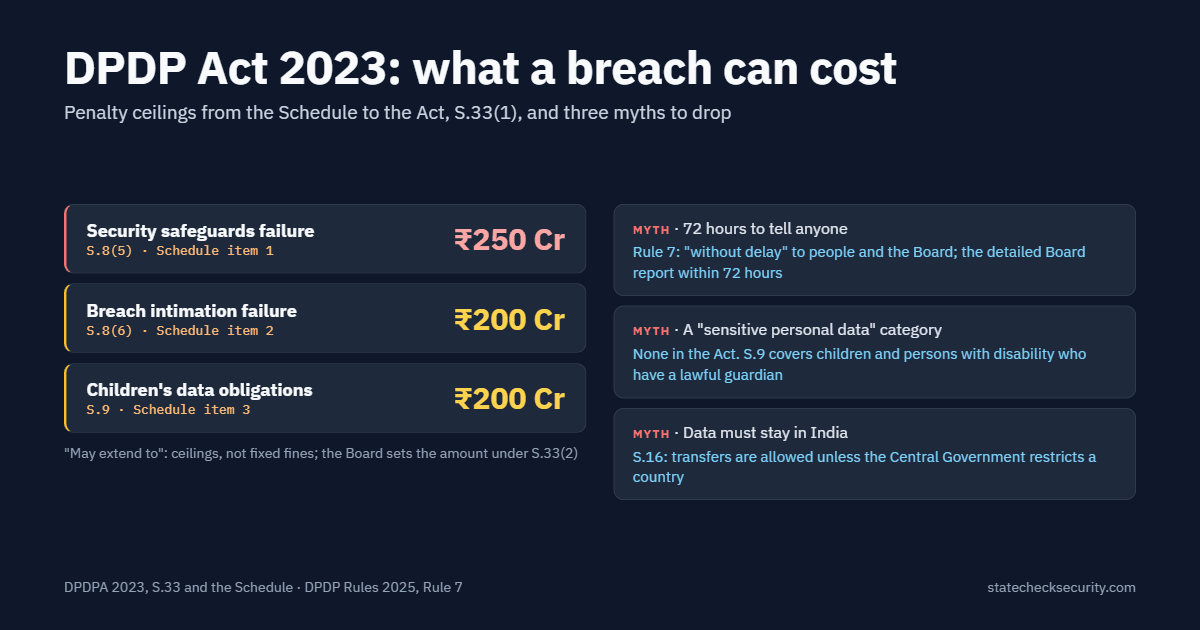
Why India's DPDP Act 2023 Matters: Data Breach Management and Customer Trust
Key Takeaways - The DPDP Act 2023 imposes up to ₹250 crore in penalties for failure to implement security safeguards under Section 8(5) — the highest single ceiling in the Act — and a separate ₹200 cr
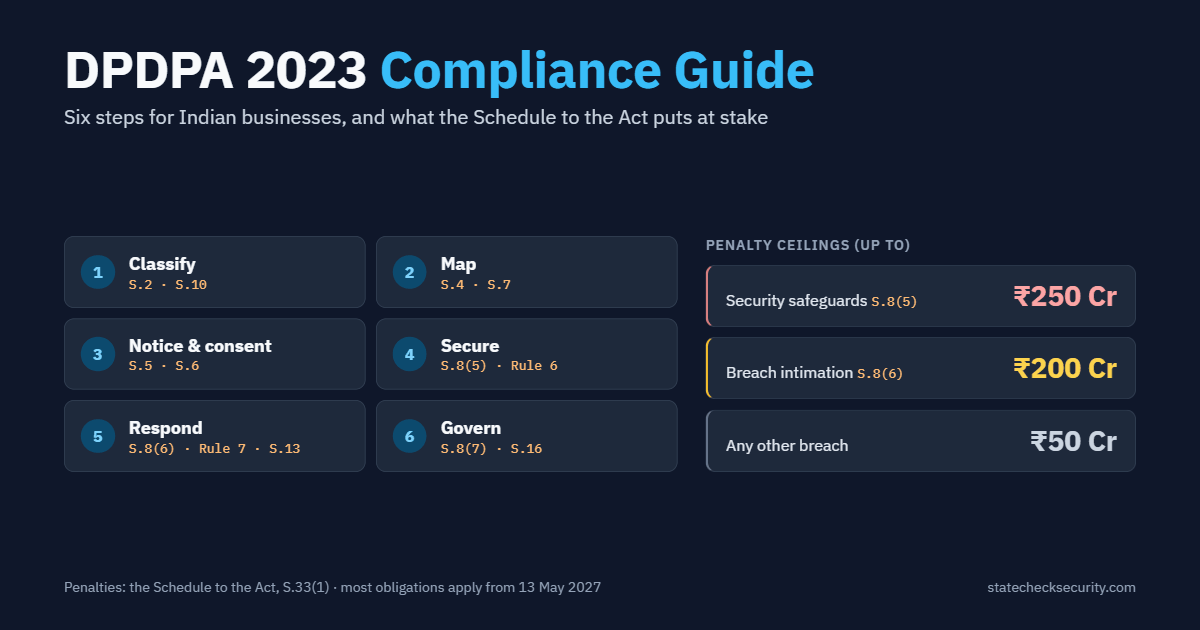
DPDPA Compliance Guide for Businesses (2023)
Key Takeaways - Every organisation that decides the purpose and means of processing personal data is a Data Fiduciary under DPDPA — including SaaS vendors, fintech platforms, e-commerce operators, and
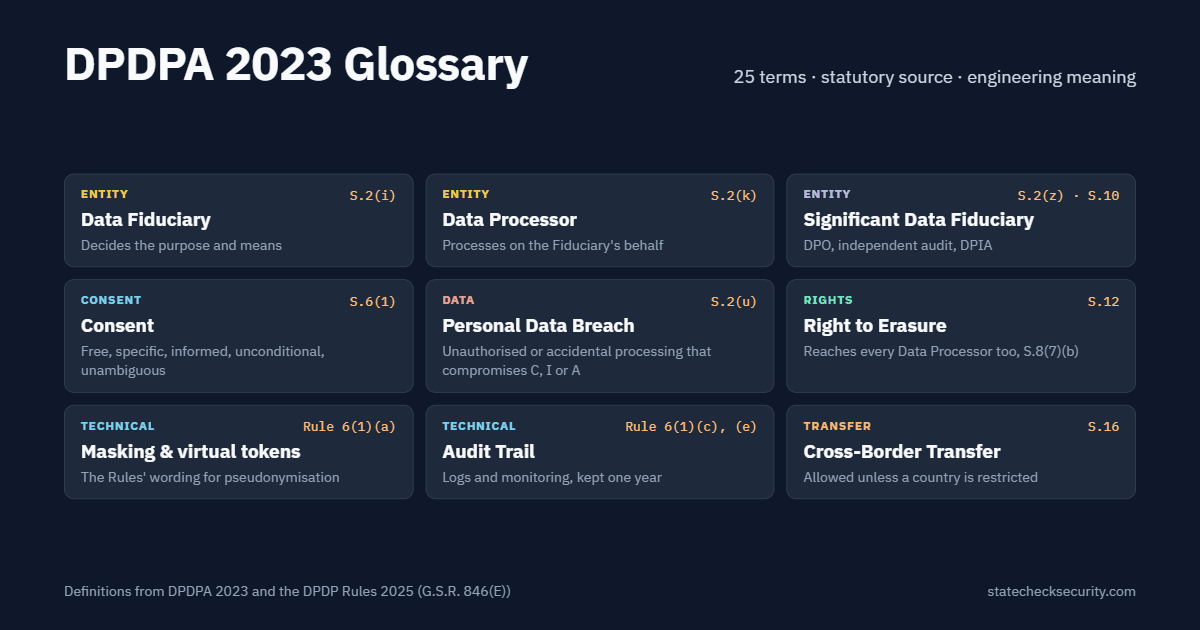
DPDPA Glossary 2023: Every Key Term Defined for Engineering and Legal Teams
Key Takeaways - Misidentifying your compliance role — Data Fiduciary vs.
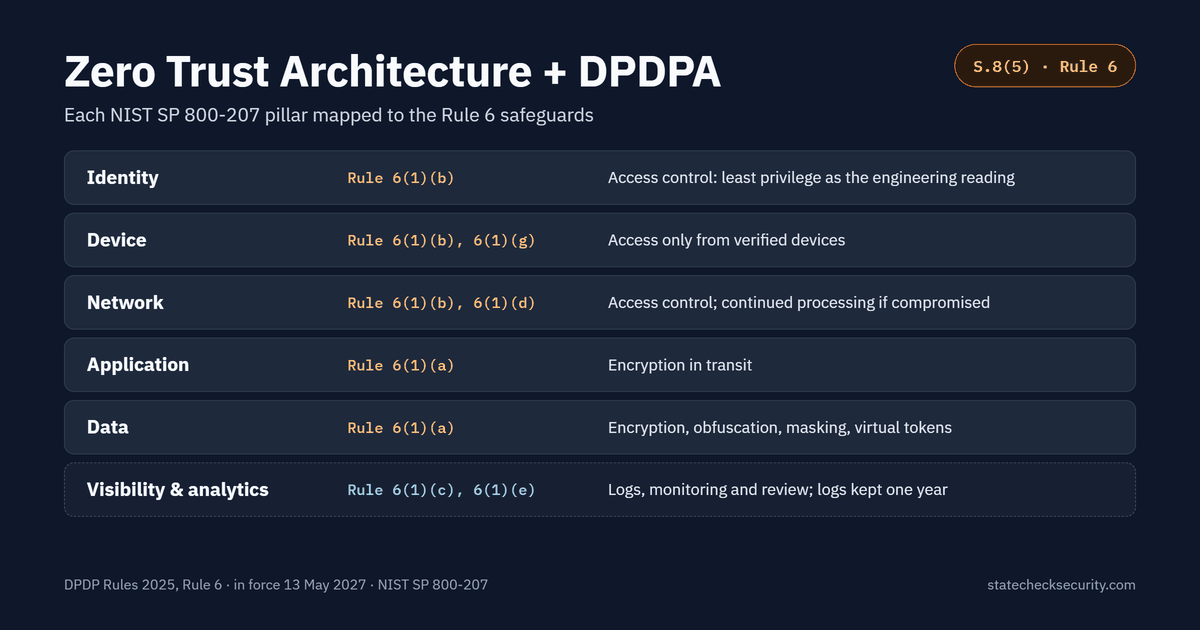
Zero Trust Architecture as a DPDPA Compliance Enabler
DPDPA Rule 6(1)(b) requires "appropriate measures to control access to the computer resources" that process personal data.
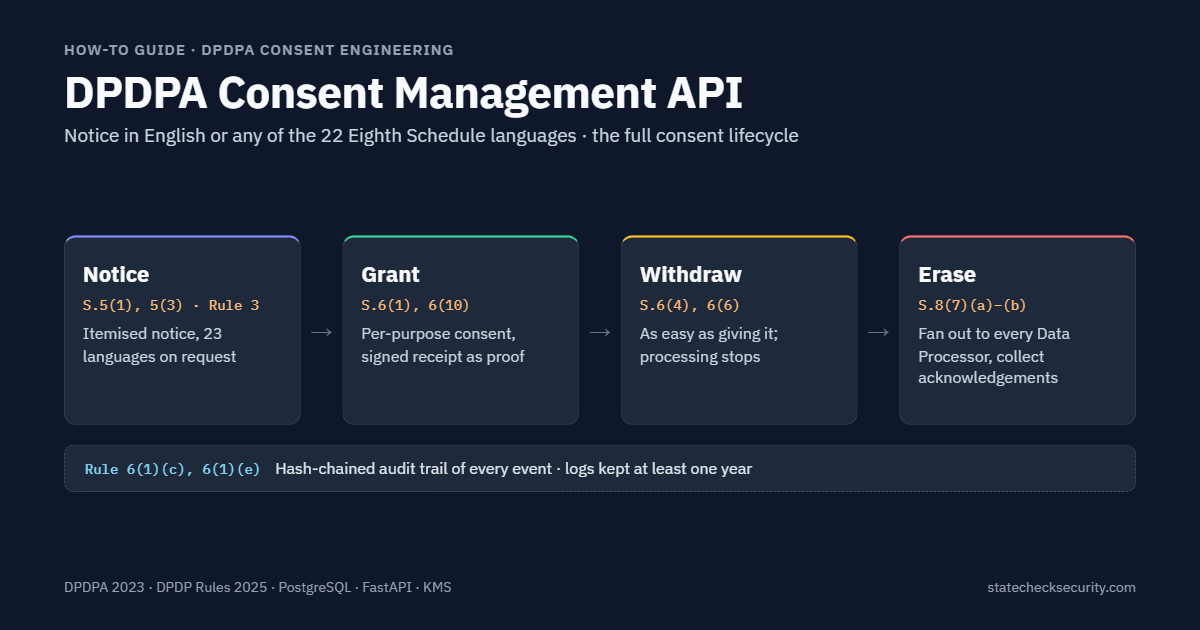
DPDPA Consent Management API: Technical Architecture for 22 Eighth Schedule Languages and English
A DPDPA consent management API must do three things GDPR tooling does not: serve consent notices in any of the 22 Eighth Schedule languages or English on demand, cryptographically bind the exact notic
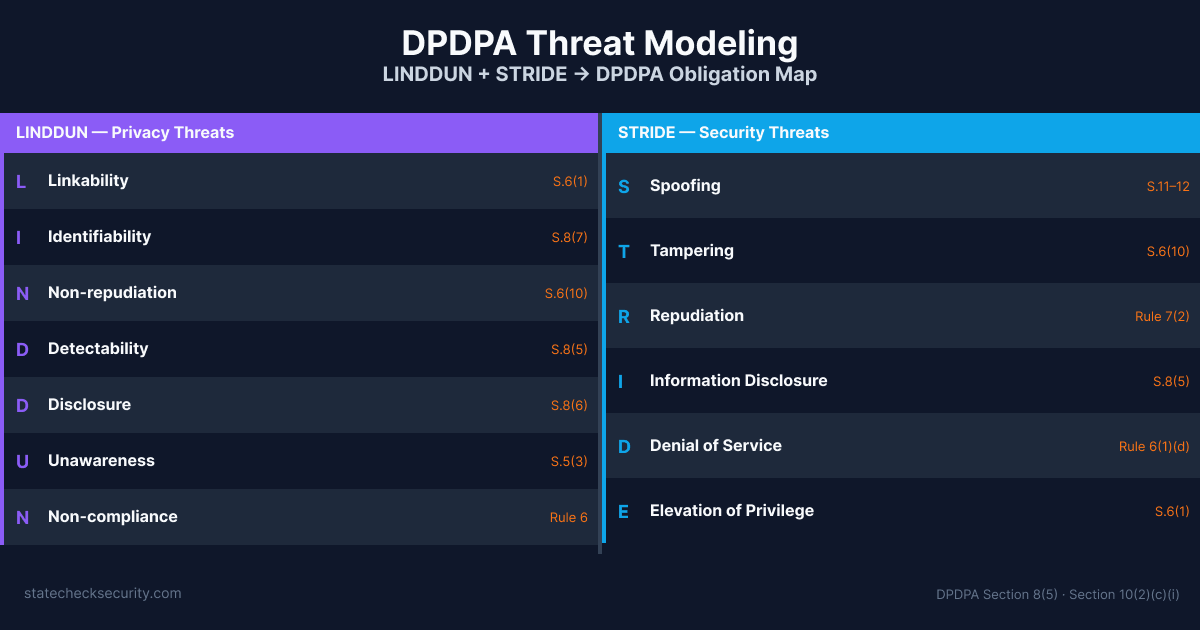
DPDPA Threat Modeling with LINDDUN and STRIDE: A DPIA-Ready Methodology
DPDPA Section 8(5) demands "reasonable security safeguards" — a standard satisfied by evidence of structured threat analysis, not just an ISO 27001 certificate.
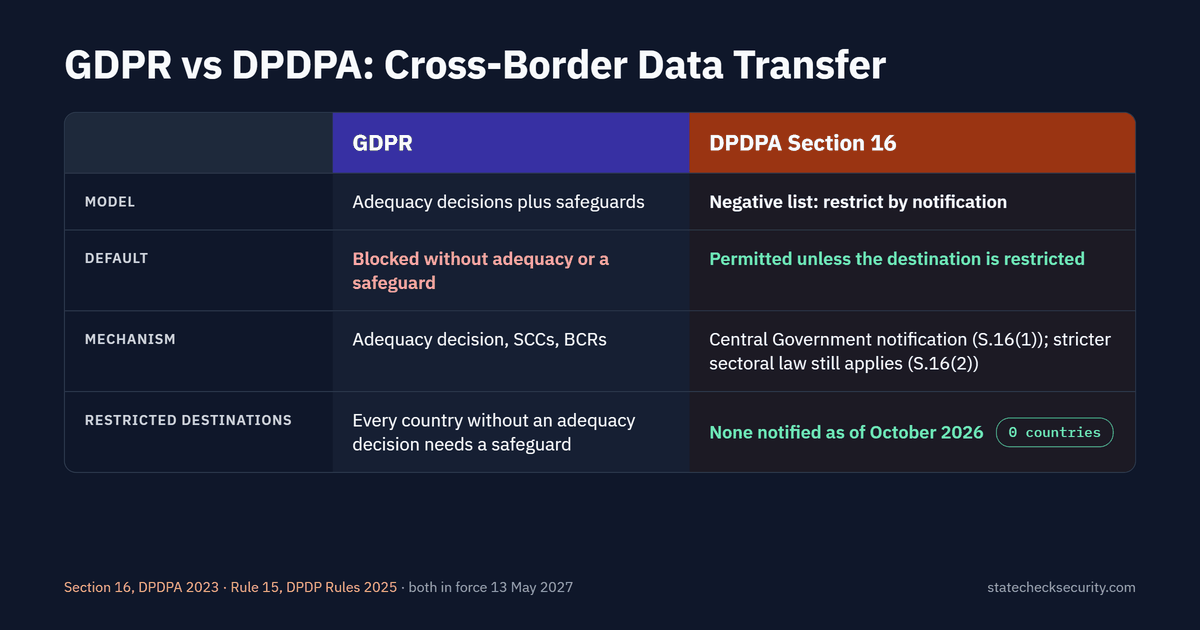
GDPR SCCs vs. India's DPDPA Cross-Border Data Transfer Rules: A Technical Comparison
GDPR and DPDPA use opposite transfer models: GDPR blocks transfers by default (whitelist/adequacy), while DPDPA permits transfers by default (negative list/blacklist).
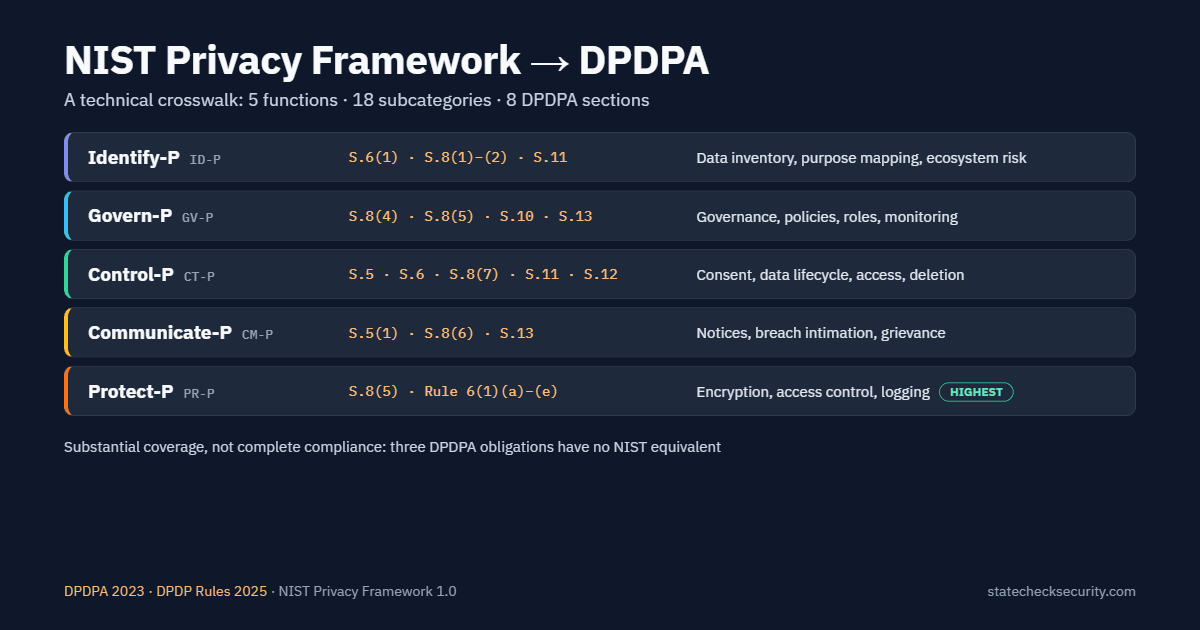
NIST Privacy Framework to DPDPA: A Technical Crosswalk
The NIST Privacy Framework's five functions map to 18 subcategories across 8 DPDPA sections — substantial coverage but not complete compliance.
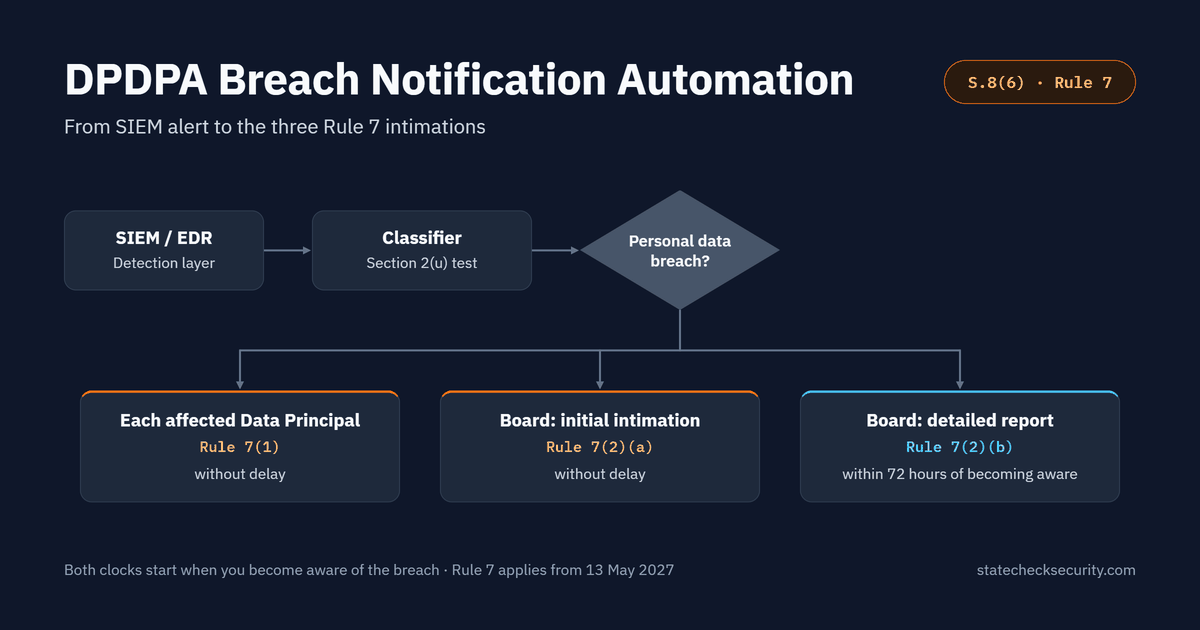
DPDPA Breach Notification: Automating SIEM Alerts to Legal Workflows
DPDPA breach intimation under Rule 7 runs two clocks: "without delay" to Data Principals and the Board, then a detailed Board report within 72 hours.
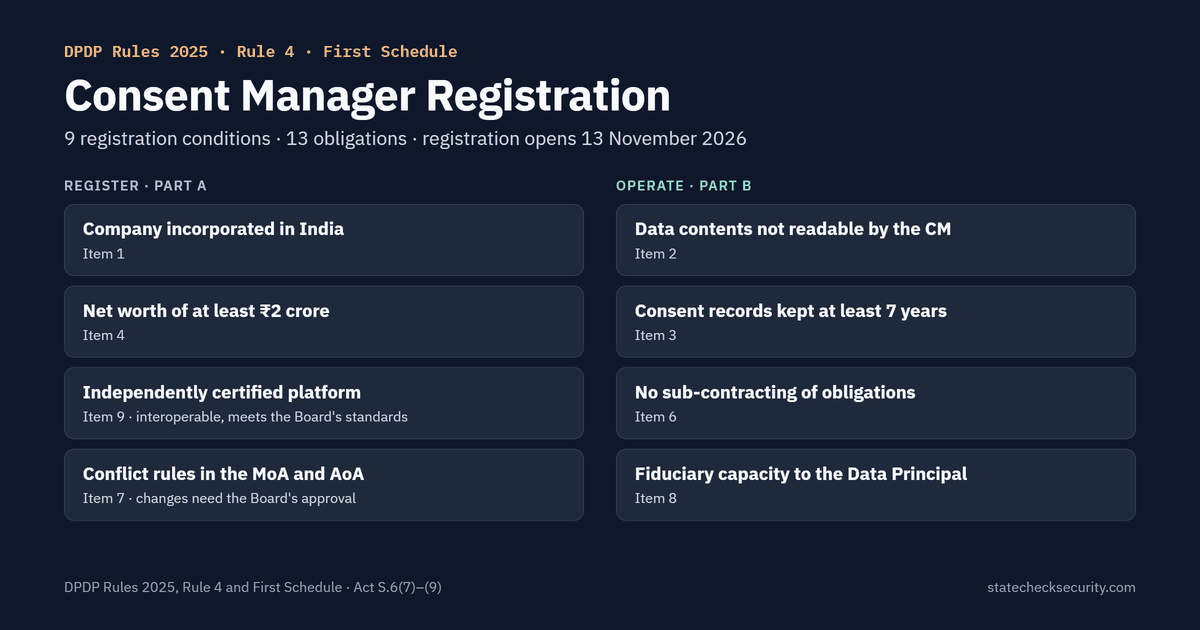
Consent Manager Registration Under DPDPA: Technical Requirements and Infrastructure Mandates
The DPDPA creates a wholly new regulated entity type — the Consent Manager — with no direct equivalent in GDPR or CCPA.
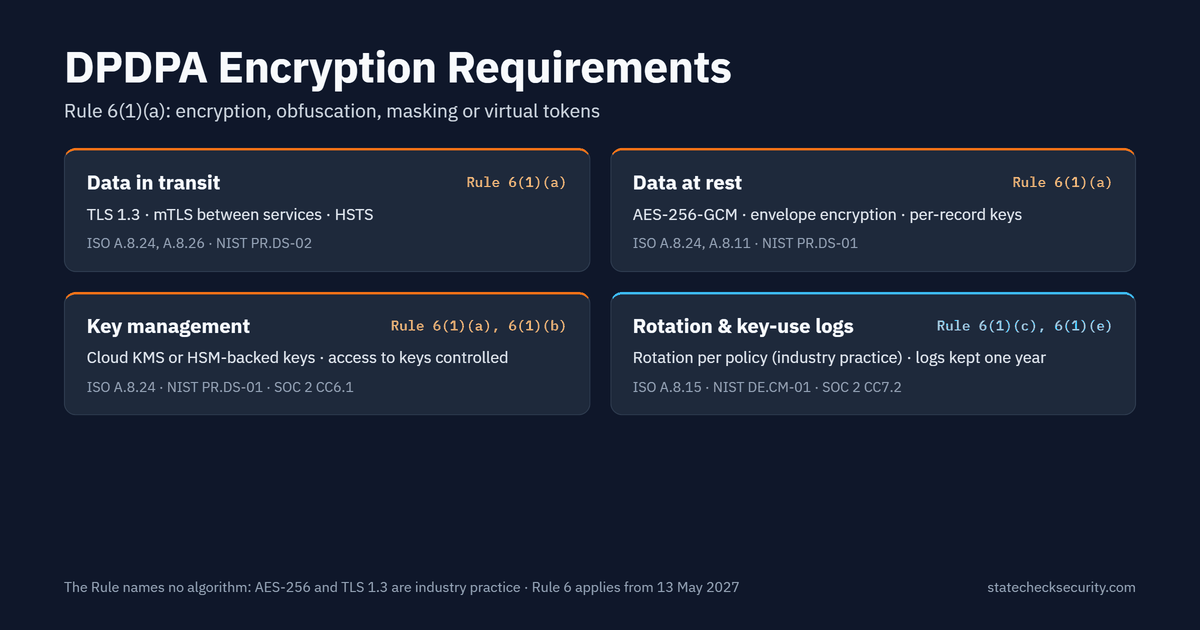
Implementing Cryptographic Controls for DPDPA: Encryption Standards at Rest and in Transit
Rule 6(1)(a) of the DPDP Rules 2025 names encryption first among the minimum "reasonable security safeguards," alongside obfuscation, masking and virtual tokens — the wording is "securing of personal
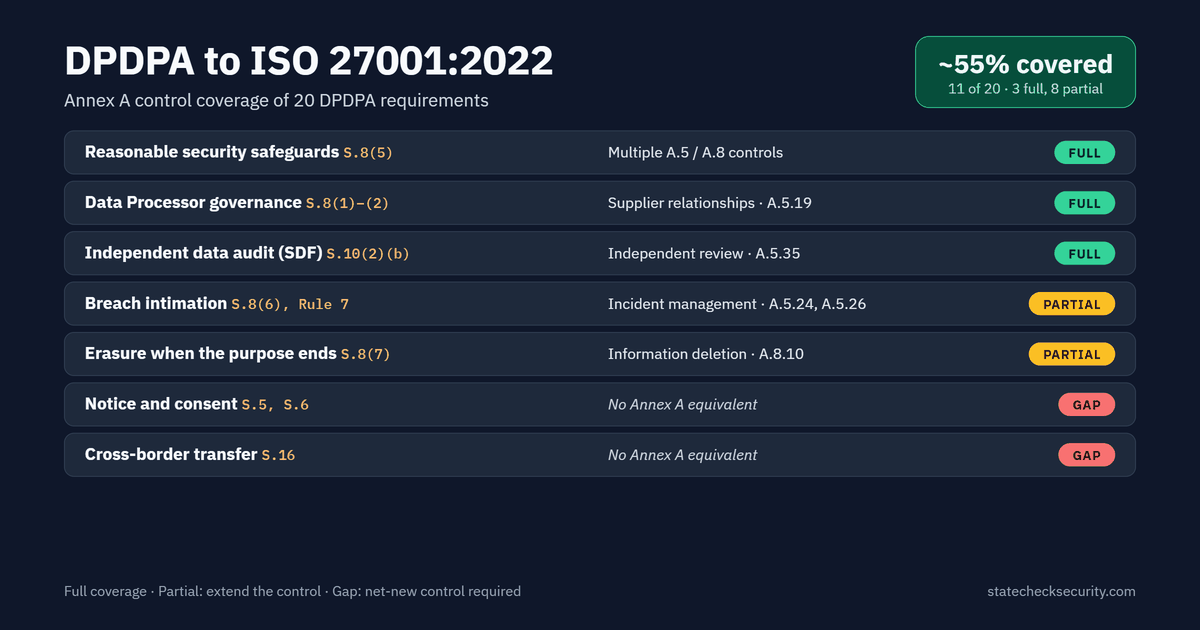
The DPDPA to ISO 27001 Mapping Guide: Leveraging Annex A for Privacy Compliance
ISO 27001:2022 covers approximately 55% of DPDPA's technical obligations — 11 of 20 granular requirements, with 3 at full coverage and 8 at partial coverage.
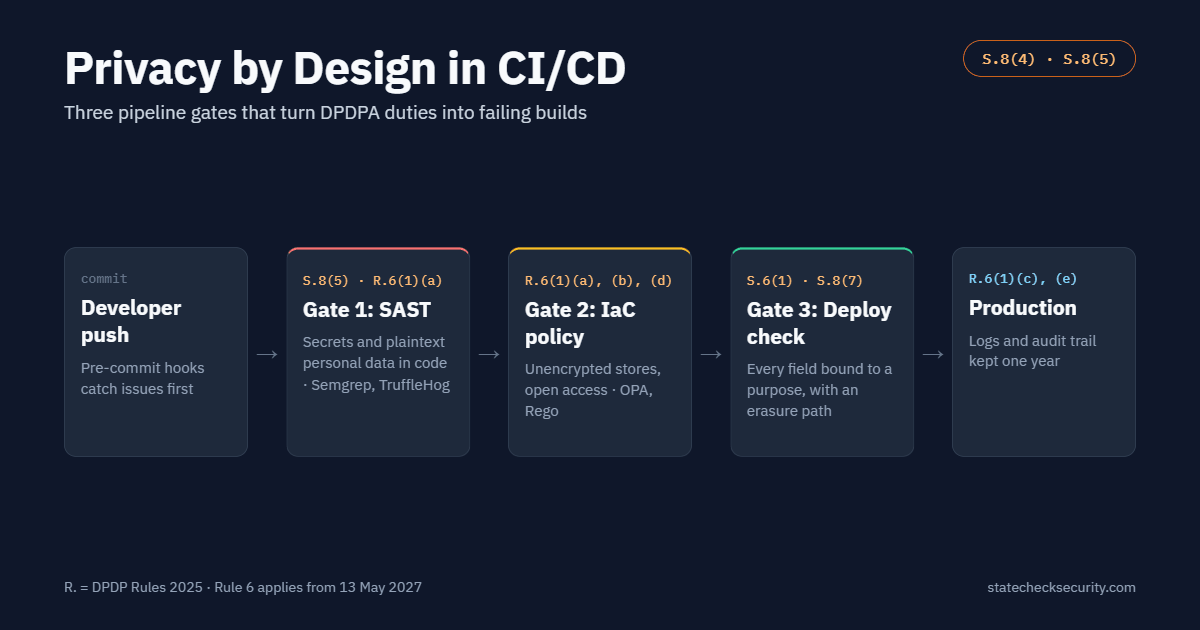
Engineering Privacy by Design: Implementing DPDPA at the CI/CD Pipeline
Section 8(4) of the DPDPA is the statutory mandate for privacy by design: it requires Data Fiduciaries to implement "appropriate technical and organisational measures" — automated CI/CD gates are a di
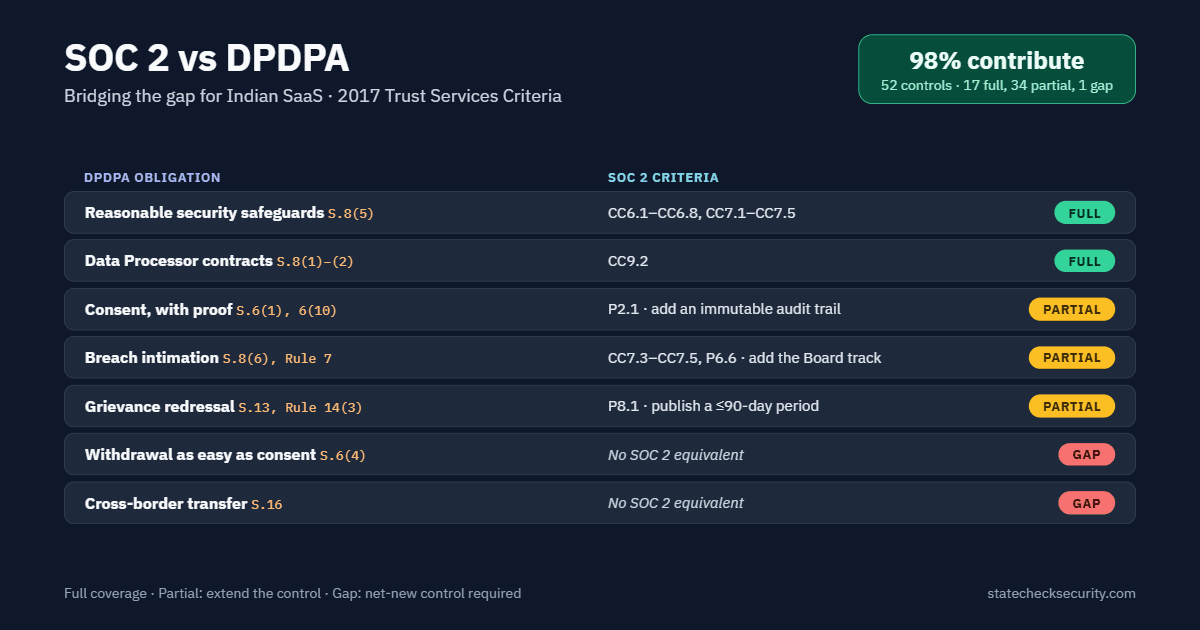
SOC 2 Privacy Criteria vs. DPDPA: Bridging the Gap for Indian SaaS Companies
SOC 2 controls contribute to 98% of DPDPA compliance obligations — 33% provide full alignment, 65% need DPDPA-specific extensions, and only 2% are pure gaps with no SOC 2 equivalent.